
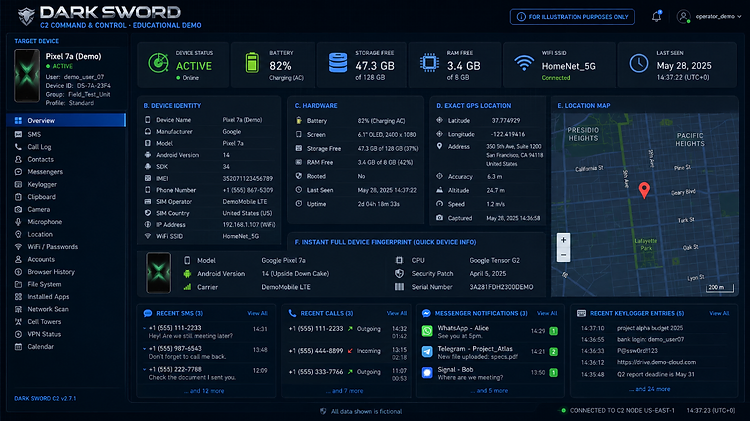
Illustrative C2 dashboard interface — for demonstration purposes only. All data shown is fictional.
C2 Dashboard for Spy Phone Surveillance
A unified command-and-control dashboard delivering real-time remote access to 20 cyber-intelligence capabilities on hardware-modified spy phones — from message interception to ambient audio, location, and credential capture.
The Command and Control Dashboard
Your PC remotely controls the Samsung device through the C2 dashboard for remote surveillance and lawful interception. The Overview page delivers a single-screen technical fingerprint of the monitored device — everything you need to assess its state, exposure, and operational value.
Device Telemetry Captured
This feature gives the operator an immediate technical fingerprint of the device. It helps identify the exact phone model, Android version, carrier, connectivity state, and whether the device is currently active. In a threat-analysis context, this information can be used to determine the device's exposure level, possible vulnerabilities, privilege state, and operational value — all from a single consolidated view.
Remote Surveillance Capabilities
Each module operates over a single authenticated command-and-control session on the hardware-modified device.
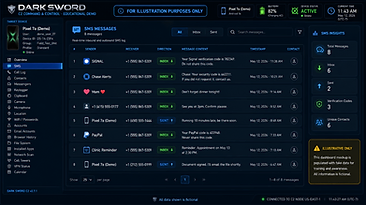
SMS Monitoring Page
The SMS module displays inbound and outbound messages. For each message it captures sender number, receiver number, full message content, timestamp, and direction — received or sent.
SMS access is highly sensitive because SMS is still widely used for one-time passwords, banking alerts, verification codes, appointment confirmations, account recovery, and private communications. Intercepting this channel provides a comprehensive view of the target's authentication activities and personal correspondence.
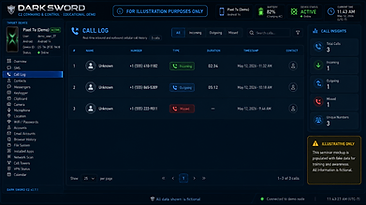
Call Log Page
The call log module displays incoming, outgoing, missed, rejected, and unknown calls. It may include the contact name, phone number, call type, call duration, date, and exact time.
Call logs expose relationship patterns. Even without recording the call content, call metadata can reveal who the user communicates with, how often, and at what times. It reveals social structure, habits, and trusted relationships.
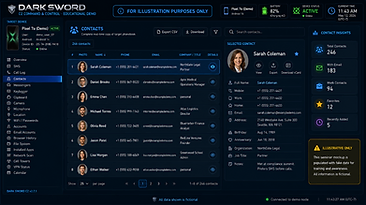
Contacts Page
The contacts module extracts the full phonebook — names, phone numbers, email addresses, physical addresses, birthdays, notes, contact photos, organizations, and job titles. Includes search and export functions for operational use.
A full contact list gives the operator a ready-made map of the target's personal and professional network. Once the phonebook is exposed, access may expand beyond the individual device to an entire organization, family, or business network.
Messengers / Notification Monitoring Page
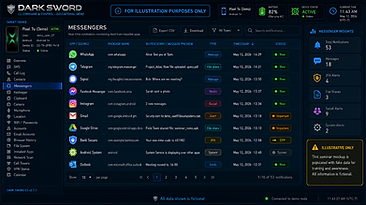
The messenger module monitors notifications from WhatsApp, Signal, Telegram, Facebook Messenger, Gmail, Google Drive, and other applications — displaying package names, notification text, message previews, timestamps, file-sharing alerts, system notifications, and push alerts.
Even where full encrypted chat extraction is not possible, notification content may still reveal message previews, OTP codes, sender names, banking alerts, and sensitive context. This module provides real-time visibility into communications across multiple apps simultaneously.
Keylogger Page
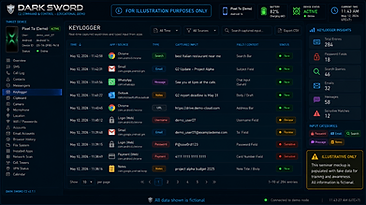
The keylogger module records typed input across apps — capturing passwords, login details, search queries, emails, credit card numbers, and other text entered into the device.
A keylogger turns the phone into a credential-harvesting device. It can defeat many security controls because it captures secrets at the exact moment the user enters them — bypassing encryption, password managers, and two-factor authentication alike.
Clipboard Monitoring Page
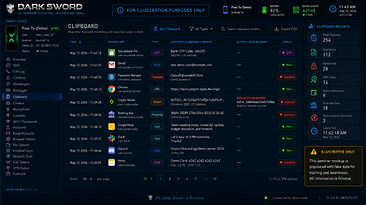
The clipboard module reads copied content and may also replace it. It captures passwords, links, crypto addresses, OTP codes, bank details, IBANs, credit card data, private messages, and copied images or text.
The clipboard is often used as a temporary bridge between apps. Users copy passwords, crypto addresses, bank details, verification codes, and private content without realizing that the clipboard can be monitored — or actively manipulated.
Camera Page
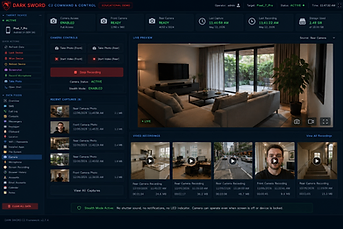
The camera module allows remote use of the front camera, rear camera, or both — taking photos, starting or stopping video recording, uploading captured media to the dashboard, previewing content, and downloading files.
Camera access converts the smartphone into a visual surveillance sensor — enabling capture of sensitive documents, observation of people nearby, exposure of the user's home or office, and collection of compromising images or videos.
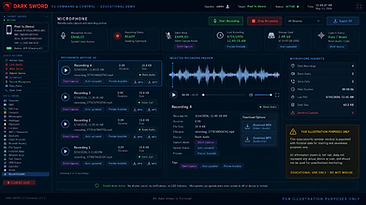
Microphone Page
The microphone module supports remote audio recording, including room audio and possibly voice-call audio. The dashboard displays date/time, duration, file size, filename, audio preview, and download options such as MP3 or MP4.
Microphone access enables covert collection of conversations near the phone — exposing meetings, private conversations, business negotiations, legal discussions, medical conversations, family conversations, and calls.
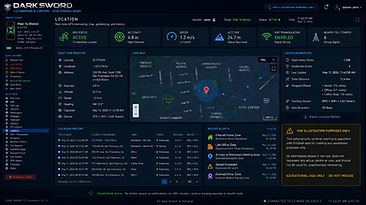
Location / GPS Page
The location module displays latitude, longitude, address, accuracy, altitude, speed, map view, and location history — including live updates, historical tracking, and geofencing-style alerts.
Location tracking connects digital compromise to physical surveillance — enabling stalking, exposure of home and work addresses, identification of routines, tracking of family locations, monitoring of travel, and timing of physical or cyber operations.
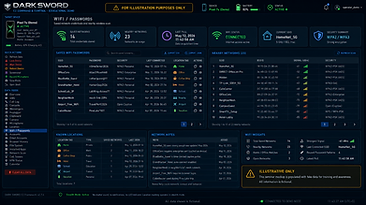
WiFi / Passwords Page
The WiFi module lists saved WiFi networks and may expose WiFi passwords. It also shows nearby networks with SSID, BSSID, signal strength, and security type.
WiFi data connects the phone to the user's physical locations and networks. Saved WiFi names may reveal home, office, hotels, airports, schools, and other places the user has visited.
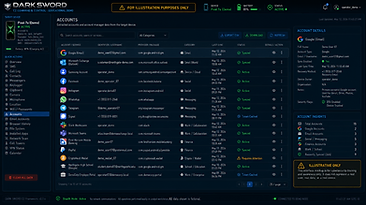
Accounts Page
The accounts module lists accounts configured on the Android device — including Google/Gmail, Outlook, Yahoo, corporate Exchange, manufacturer accounts, social media, messaging apps, work accounts, school accounts, banking/finance apps, and other apps integrated with Android account management.
Even without passwords, knowing which accounts exist on a device is valuable intelligence. It allows attackers to tailor phishing messages and account-recovery attacks with precise targeting.
Email Accounts Page
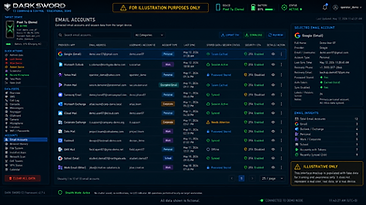
The email accounts module displays configured email addresses, provider type, username, last sync time, and possibly authentication-related data if accessible.
Email accounts are often the central recovery mechanism for banking, social media, cloud storage, crypto exchanges, business platforms, and identity services. Email compromise can become a master key.
Browser History Page
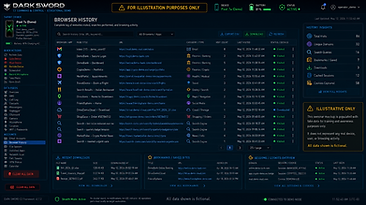
The browser history module displays visited websites, page titles, timestamps, visit counts, search queries, downloads, bookmarks, cookies, cached sessions, form data, and other browser artifacts.
Browser data reveals interests, intentions, sensitive services, financial activity, medical searches, private behavior, and possible logged-in sessions — including profiling, blackmail leverage, and identification of crypto or banking platforms.
Screen Time / App Usage Page
The screen time module displays total screen-on time, app usage duration, number of app launches, daily/weekly/monthly charts, and a list of apps opened by the user.
App usage data creates a detailed behavioral profile of the user — revealing which banking apps, crypto wallets, dating apps, work tools, password managers, and 2FA apps they rely on daily.
File System Page
The file system module provides access to device storage — displaying photos, videos, audio recordings, documents, downloads, screenshots, APK files, hidden files, system files, and messenger media folders such as WhatsApp, Telegram, Signal, Facebook Messenger, and Instagram.
File access is one of the most powerful capabilities — exposing private media, business files, identity documents, contracts, invoices, wallet files, and received attachments. It enables data theft, extortion, intellectual property theft, and tampering with files remotely.
Installed Apps Page
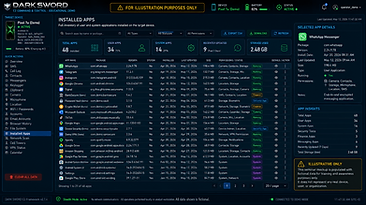
The installed apps module lists user-installed and system apps — including app name, package name, version, install date, last update date, app size, permissions, and running status.
Installed app inventory provides reconnaissance about the user's habits, financial services, security tools, work platforms, and possible defensive software — enabling target selection, security evasion, and tailored phishing campaigns.
Network Scan Page
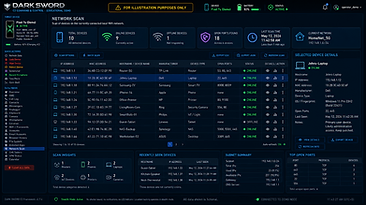
The network scan module scans the local WiFi network to which the phone is connected — displaying IP addresses, MAC addresses, hostnames, manufacturers, device types, online/offline status, and open ports.
The phone becomes a reconnaissance point inside the local network — enabling mapping of home or office devices, identification of laptops, smart TVs, cameras, printers, routers, and IoT devices, and preparation for lateral movement attacks.
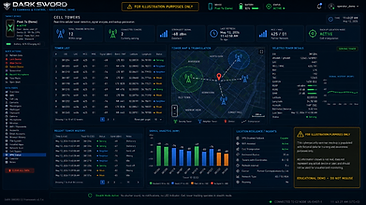
Cell Towers Page
The cell towers module displays nearby and connected cellular towers — including Cell ID, Location Area Code, Mobile Country Code, Mobile Network Code, signal strength, tower coordinates, real-time updates, and a map display.
Cell tower data supports location tracking even where GPS is weak, unavailable, disabled, or unreliable — providing backup geolocation, movement analysis, and correlation with other signals.
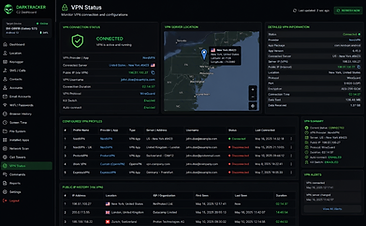
VPN Status Page
The VPN module displays connection status, provider or app name, connected server, public IP address, username, connection duration, VPN protocol, and all configured VPN profiles on the device.
VPN information reveals whether the user is attempting to mask their network location or route traffic through a privacy service — exposing the VPN provider, server location, public IP, account credentials, and configuration for potential targeting.
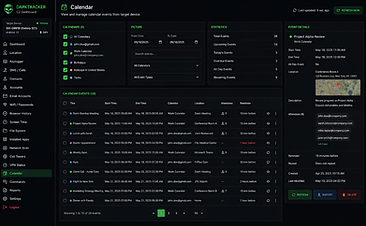
Calendar Page
The calendar module extracts events from Google Calendar, Samsung Calendar, Outlook, Exchange, and other synced calendars — including title, date, start and end time, location, description, notes, attendees, recurring events, and reminders.
Calendar access exposes the user's full schedule — meetings, travel, appointments, deadlines, and personal or professional commitments. This enables physical stalking, timed phishing attacks, business intelligence gathering, and targeted intrusion planning.
C2 Data Flow Schematic
Illustrative architecture only — no live data, device identifiers, or operational details are shown. This diagram depicts how intelligence moves from the hardware implant to the operator's C2 dashboard over a protected channel.
Diagram is a sanitized representation. Actual C2 interfaces, device identifiers, and operational telemetry are withheld for operator and client security.
Deploy a C2 Dashboard
Access the full command-and-control interface with 20 remote surveillance capabilities on a hardware-modified Samsung Galaxy spy phone.
Zero-Click Hardware Capabilities
A tabbed breakdown of the surveillance chipset's architecture, capabilities, persistence, and security. Sanitized specification — proprietary identifiers and firmware versions are withheld for operational security.
The surveillance layer is a dedicated cyber-intelligence coprocessor embedded on the device mainboard, physically and logically beneath the Android operating system.
- Base Platform
- Genuine Samsung Galaxy flagship smartphone (unmodified external appearance)
- Intelligence Layer
- Dedicated cyber-intelligence chipset embedded beneath the Android OS
- Execution Domain
- Separate silicon domain with its own firmware, storage, and boot ROM
- Isolation Boundary
- Asymmetric visibility — coprocessor reads OS/peripherals; OS cannot enumerate coprocessor
- Device-Tree Presence
- None — no driver, no bus address, no entry in the OS device tree
- Inter-Processor Bus
- Hardware-level peripheral bus tap; capture independent of app configuration
- Boot Independence
- Independent boot ROM and power domain; active before and regardless of OS boot
C2 Module Screenshots
Illustrative screenshots of each of the 20 remote surveillance modules as they appear in the DARK SWORD command-and-control dashboard. All data shown is fictional — for demonstration purposes only.



















Zero-Click spyware models, side-by-side
Hardware capabilities contrasted across our three deployment tiers — choose the platform matched to your authorized operational requirements.
| Capability | SpyPhone Recon Field Tier | SpyPhone Tactical Operational — Recommended | SpyPhone Command Flagship |
|---|---|---|---|
| Base handset | Samsung Galaxy mid-range | Samsung Galaxy S-series flagship | Samsung Galaxy S26 Ultra |
| Embedded surveillance chipset | Compact module | Dedicated cyber-intelligence chipset | Enhanced dual-core chipset |
| Intelligence storage partition | Isolated, encrypted | Isolated, encrypted | Hardware-isolated secure enclave |
| Survives factory reset | Yes | Yes | Yes |
| Survives OS updates | Yes | Yes | Yes |
| Active in airplane mode | Limited (store-and-forward) | Yes | Yes |
| Anti-forensic wipe | Optional | Standard | Standard |
| Out-of-band C2 channel | Yes | Yes | Yes |
| Hardware-isolated operator comms | Yes | Yes (encrypted) | Yes (encrypted) |
| Audit-logged commands | Yes | Yes | Yes (evidentiary) |
| Active capability count | 12 vectors | 20 vectors | 20 vectors + integrity monitoring |
| Ambient microphone activation | Yes | Yes | Yes |
| Remote camera capture | Yes | Yes | Yes |
| Keylogger & clipboard capture | Yes | Yes | Yes |
| GPS + cell-tower triangulation | GPS only | Yes | Yes |
| Encrypted courier delivery | Standard | Insured FedEx | Insured FedEx + tamper-evident |
| License model | Annual | Monthly / 6-mo / Annual | Annual + support retainer |
All models are hardware-backed and operate beneath the operating system — no software exploit, no patchable signature.
Authorized Use Only — Lawful Monitoring Required
SpyPhone hardware-modified devices are sold exclusively to vetted corporate, investigative, and compliance professionals for lawful monitoring of devices the purchaser is legally authorized to monitor. Use requires legal authority under the applicable jurisdiction. We do not sell for stalking, unlawful interception, or surveillance without consent where required by law. Every request is reviewed before procurement, and all sales are conditional on acceptance of our Legal Notice.